Hi,
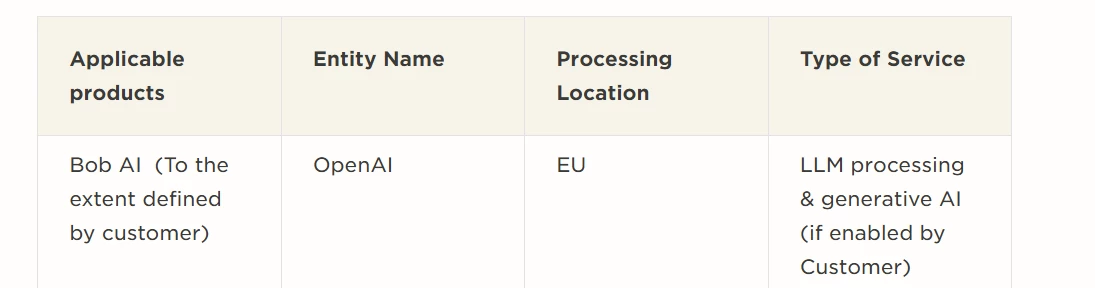
We are very interested in testing Bob's AI features but have some concerns regarding data security, specifically about where data is stored, who has access, and exactly what information is shared.
Although we've reviewed the provided documentation, some questions remain:
-
AI for Reports:
-
Managers will have access to create reports. The documentation mentions that personally identifiable information (PII) from standard fields will be anonymized. However, how will Bob handle PII in custom fields that managers may unknowingly include in their reports? Managers typically do not distinguish between standard and custom fields.
-
-
AI for Goals:
-
What type of goal-related information is extracted from Bob? Goals can contain sensitive business strategies (e.g., launching new products or expanding into new markets). Could you clarify what specific goal data is shared, and who will have access to it?
-
Given our operations in Europe, strict compliance with GDPR is essential, and transparency with employees is critical. As new AI capabilities are introduced, clear documentation specifying precisely what data is shared would be highly beneficial.
Additionally, a dedicated agreement (similar to the Data Processing Agreement but specifically covering AI-related data handling) would be very useful.
Best regards,
Øyvind